Evidence or it does not ship
Every object has a source, a confidence, a marking, and a date it dies. We do not publish atmosphere.
About Attack Nemesis
We exist because too many good reports die in a PDF, and too many SOCs are asked to be the integration layer. We started in Denver with a desk, a bias for evidence, and a rule: models draft, analysts sign.
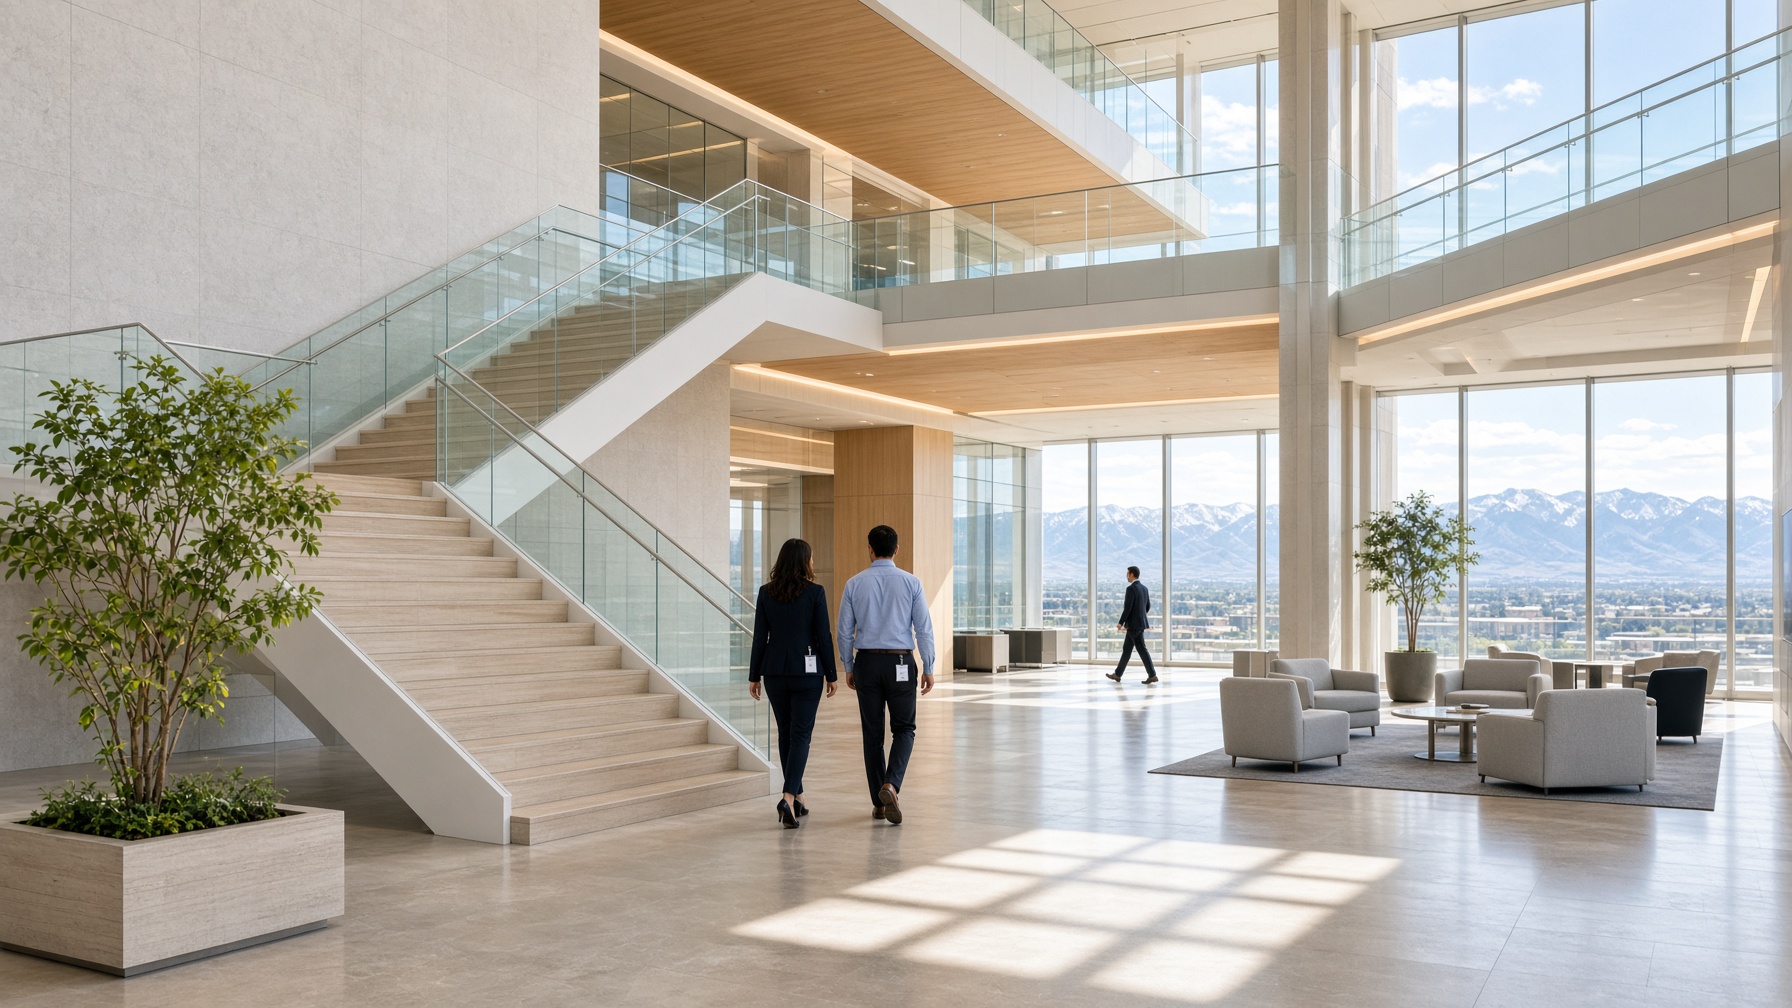
Denver, Colorado
We sell a platform and a research practice. The collections behind intake are produced here. The actions we ship are tested against those collections before they ever reach a customer SIEM. That loop is the company. The loop in four steps. The name is a reminder of the job: be the other side of the attack.
Every object has a source, a confidence, a marking, and a date it dies. We do not publish atmosphere.
Extraction and first drafts are machine work. Attribution, scoring judgment, and the decision to act stay with a named analyst.
If a report cannot become a ticket, a block, a patch, or a detection in a tool you already run, it is unfinished.
Leadership
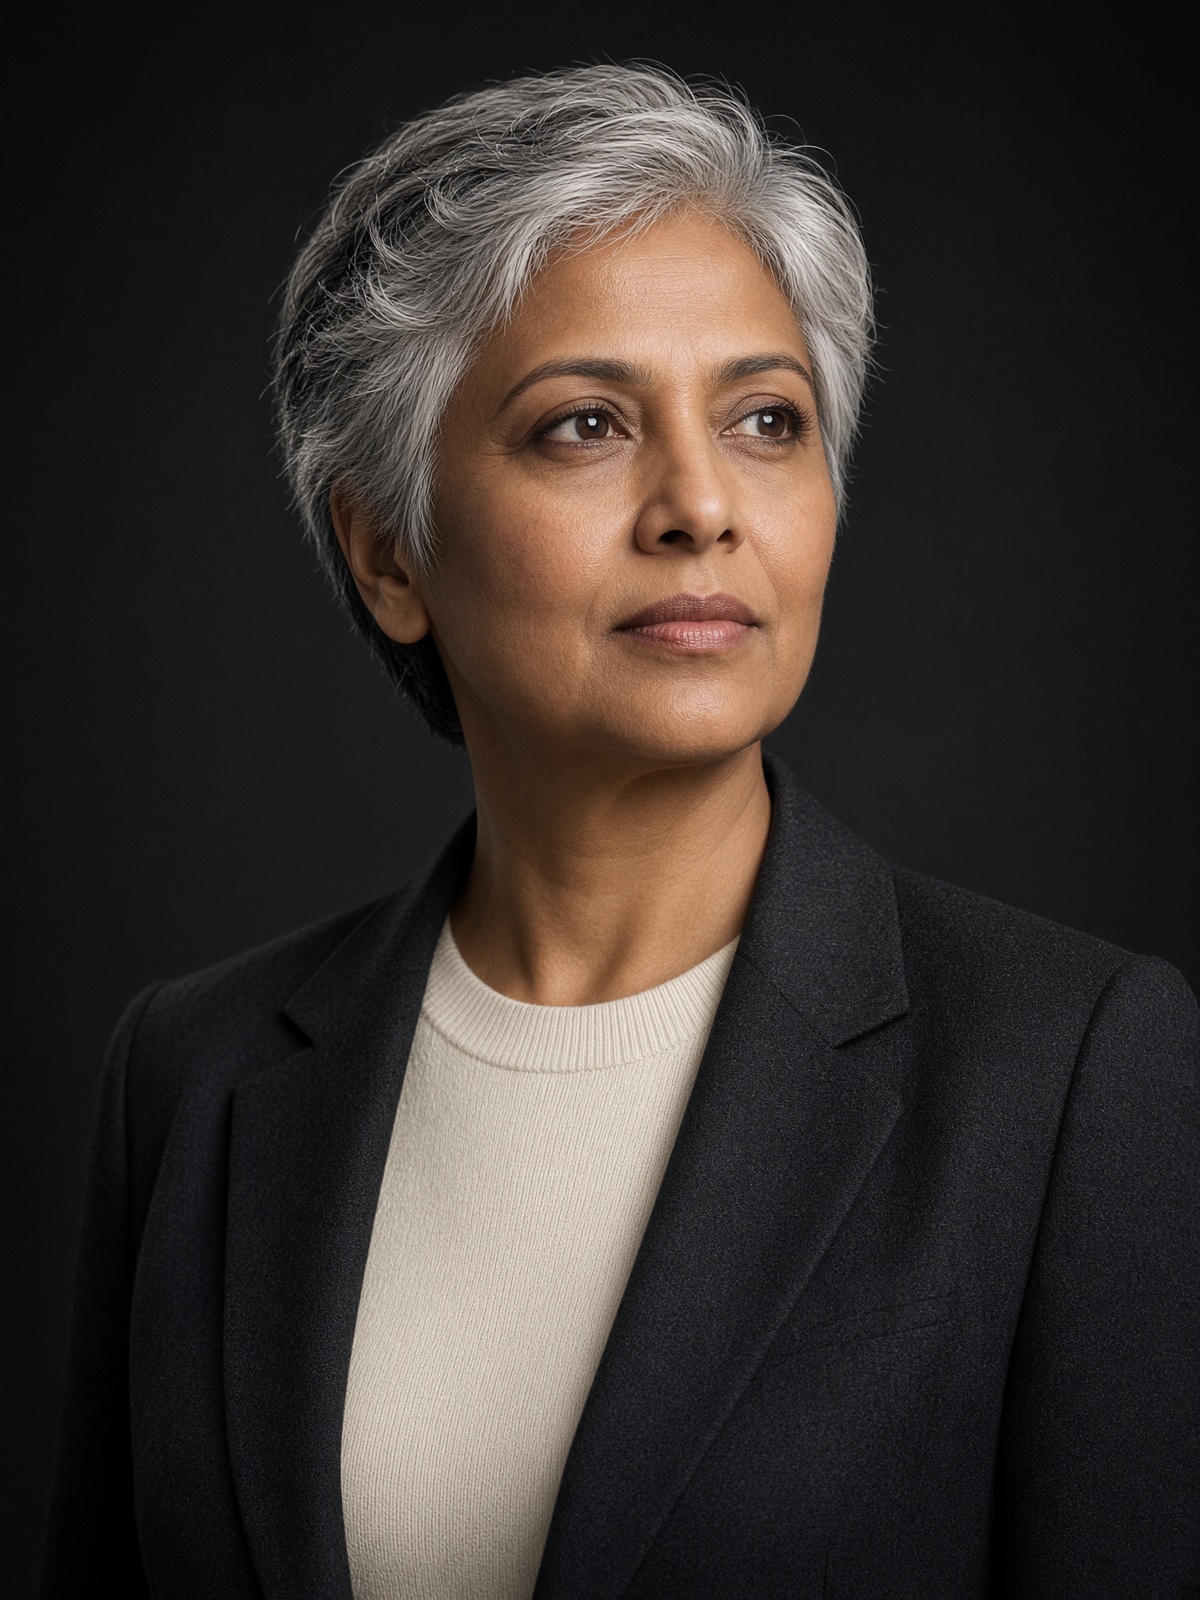
Chief Executive Officer
Mira spent fifteen years taking intelligence products to market inside two of the industry’s larger platform companies. She founded Attack Nemesis on a simple complaint: the intel was fine. The last mile into the SIEM, the scanner, and the ticket was not.
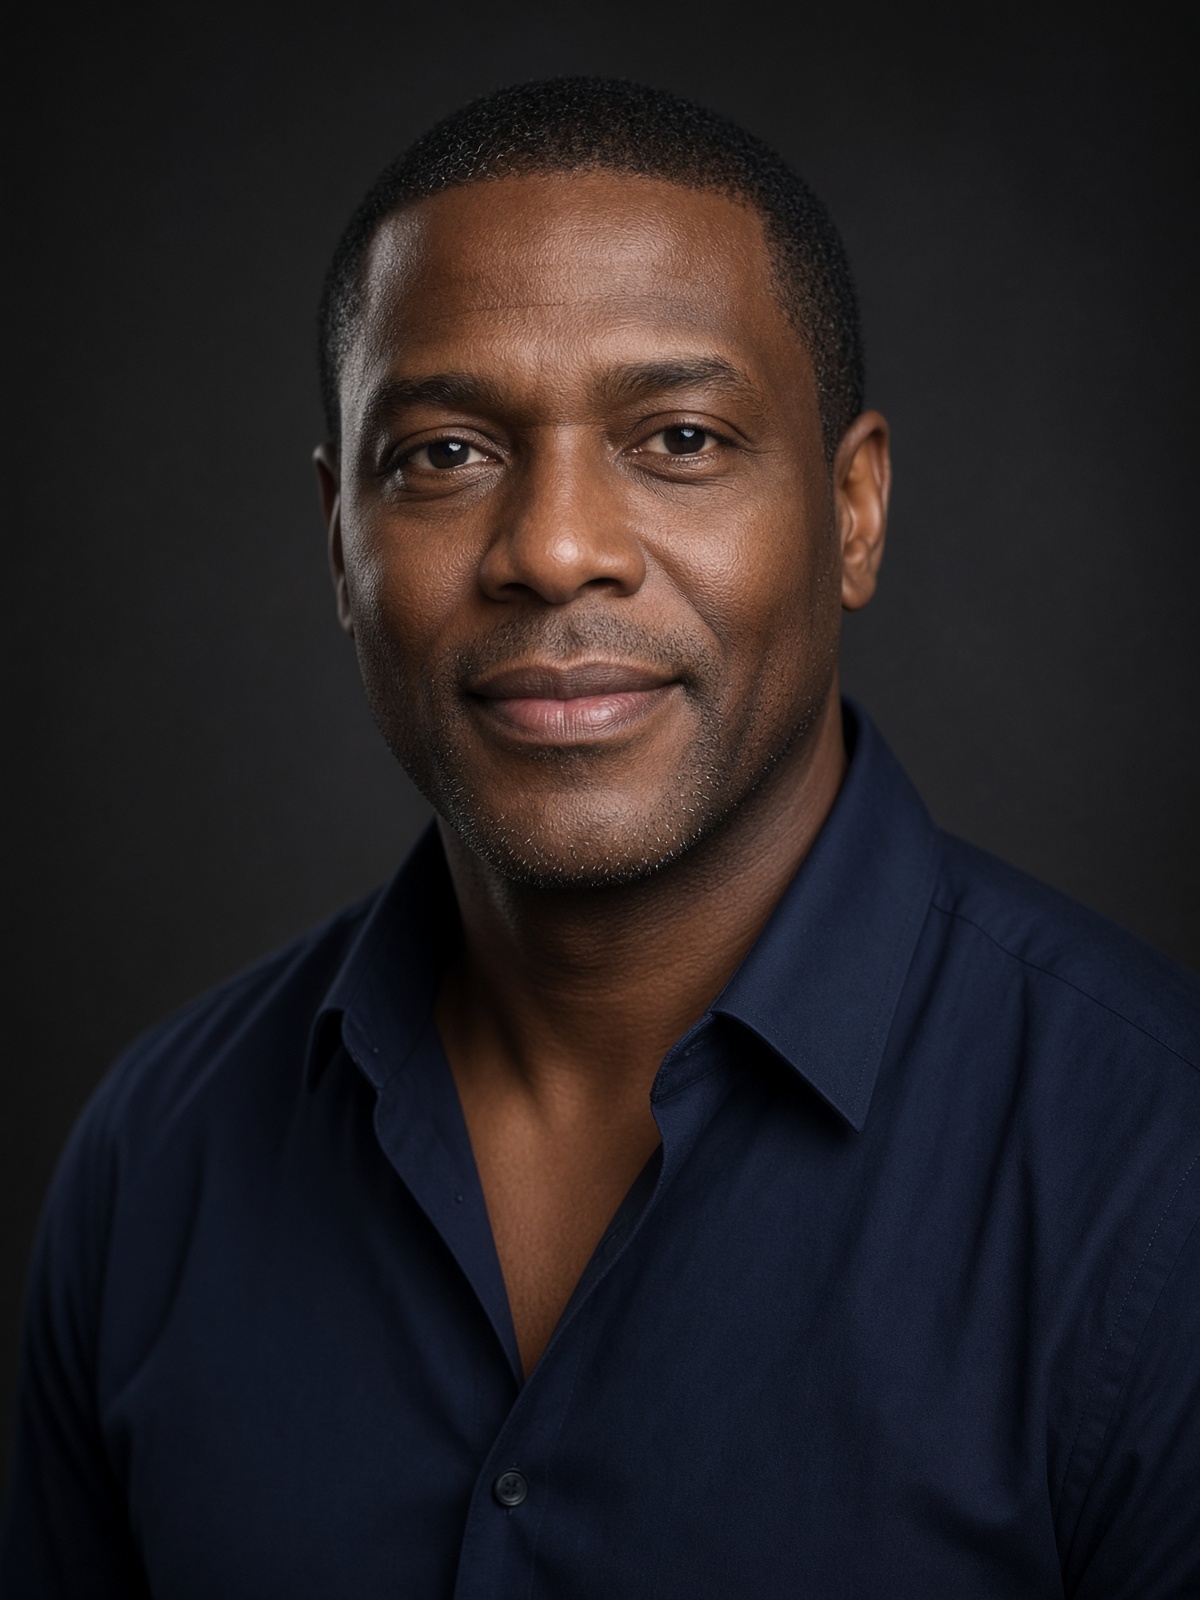
Chief Technology Officer
Julian built correlation pipelines at a national CSIRT and later led detection engineering for a global bank. The workbench is the system he wished he had when the intel team and the SOC were two floors apart.
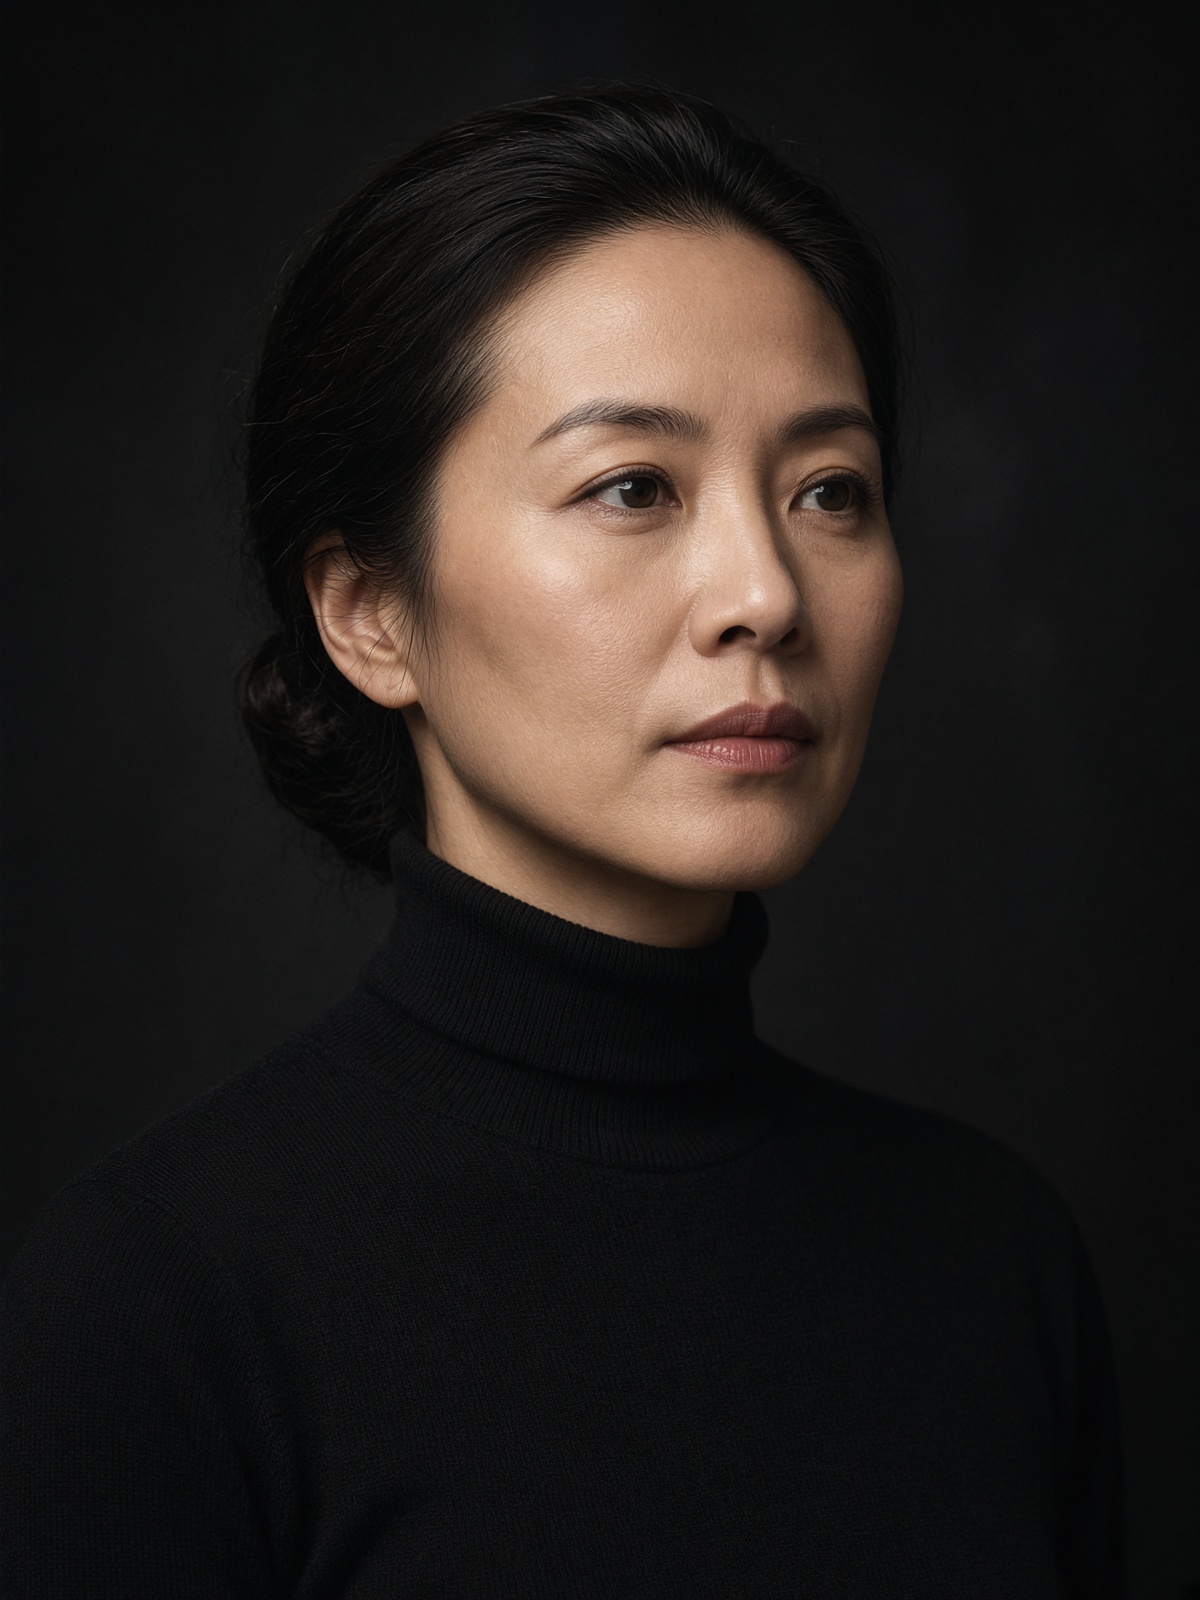
Head of Intelligence
Elena ran fusion-cell operations for a Fortune 50 manufacturer and published on analyst-in-the-loop production. She owns Attack Nemesis Research and the rule that a model does not ship an assessment.
Questions
Next step
Briefings are with the people who write the collections, not a pre-sales overlay.